When a Cyberattack Breaks the Cold Chain: How Real-Time Alerts Prevent Product Loss

A cyberattack does not need to steal data to destroy value. If an attacker can manipulate a connected refrigeration controller, the result can be a silent rise in temperature, spoiled food, damaged pharmaceuticals and a broken chain of custody.

That risk became real in France in October 2026. French authorities warned that internet-exposed refrigeration controllers had been compromised, while industry reporting described hundreds of supermarkets being affected. Attackers reportedly altered settings and triggered defrost cycles remotely. In one reported case, a cold room warmed by approximately 6°C in two hours.

The incident is a reminder that the cold chain is now cyber-physical infrastructure. Digital controls operate physical equipment, and a compromised command can quickly become a product-quality, safety and financial event.

What happened in the French refrigeration attack?

The campaign targeted connected refrigeration control systems that could be reached remotely. France’s national cybersecurity agency, ANSSI, published an alert concerning compromises involving LAE Electronic and Copeland Dixell controllers. The risk was not limited to a conventional IT outage: attackers could interfere directly with cooling operations.

According to incident reporting, the attack affected retailers across France and forced some stores to discard refrigerated products. Yet another detail is especially important for cold-chain operators: independent monitoring reportedly detected an abnormal temperature increase at a store in Bordeaux at around 4 a.m., allowing teams to intervene before the incident caused greater losses.

That is the difference between discovering an incident in a dashboard and discovering it in a warehouse full of spoiled goods.

The controller cannot be the only source of truth

Traditional refrigeration supervision often depends on the same controller that operates the equipment. That creates a dangerous dependency. If the controller is compromised, unavailable or reporting misleading values, the monitoring layer may fail at exactly the moment it is needed most.

An independent IoT sensor provides a separate source of physical truth. It measures what is actually happening around the product: temperature, humidity, location, movement or door activity, depending on the deployment. It does not need to trust the refrigeration controller’s command history.

This distinction matters. A controller may report that a setpoint is correct while an independent sensor shows that the cargo or storage area is getting warmer. The mismatch itself becomes actionable evidence.

How Sensefinity real-time alerts can expose the attack

Sensefinity’s role is not to replace firewalls, secure remote access, patch management or an incident-response team. It adds an independent detection and response layer focused on the condition of the goods.

A Sensefinity deployment can help identify the operational signature of a refrigeration attack through:

  • Threshold alerts: teams are notified when temperature or humidity leaves the permitted range, rather than waiting for a manual inspection.

  • Rate-of-change alerts: a rapid and unusual rise can trigger action before a maximum temperature threshold is reached.

  • Continuous monitoring: anomalies can be detected during nights, weekends and other periods when no employee is physically present.

  • Independent measurements: sensor data can be compared with the refrigeration system’s own readings to reveal discrepancies.

  • Fleet-wide pattern detection: simultaneous or similar anomalies across several stores, cold rooms, trailers or containers can indicate a coordinated event rather than an isolated mechanical failure.

  • Escalation workflows: alerts can be routed to the people responsible for operations, quality and security, reducing the time between detection and intervention.

Sensefinity does not need to identify the malware to protect the cargo. It detects the physical consequence of the attack early enough for people and automated workflows to respond.

From alert to damage prevention

A useful alert must lead to a predefined action. When an independent sensor detects unexpected warming, the response playbook can include:

  1. Confirm the anomaly using independent sensor data.

  2. Notify the store, warehouse or transport operator immediately.

  3. Move vulnerable products to a verified cold zone or activate backup refrigeration.

  4. Isolate remote access to the affected controller and involve the cybersecurity team.

  5. Preserve the temperature history, alert timeline and response actions for quality, insurance and forensic review.

Minutes matter. Early detection can prevent an entire load or cold room from crossing its permitted exposure limit. Even when some temperature deviation occurs, a continuous record helps quality teams determine which products remain safe instead of discarding everything because the history is unknown.

Building a cyber-resilient cold chain

Cybersecurity and cold-chain monitoring should no longer be treated as separate disciplines. A resilient architecture combines secure controllers and networks with independent condition monitoring at the asset, shipment or storage-zone level.

Operators should reduce internet exposure, change default credentials, secure VPN access, apply vendor updates and segment operational technology networks. But they should also assume that preventive controls can fail. Independent real-time sensors provide the final verification layer: Is the product still within specification?

The French incident shows why that question must be answered continuously. A cyberattack may begin in a remote-access interface, but the financial damage appears in pallets, cabinets, trailers and containers. The fastest way to limit that damage is to detect the physical anomaly while there is still time to act.

Protect the product, not only the network

Sensefinity gives cold-chain operators real-time visibility into the condition and location of goods, with alerts designed to turn abnormal conditions into immediate action. By maintaining an independent record of what the cargo actually experienced, companies can respond faster, reduce waste and strengthen evidence across the chain of custody.

If your refrigeration controls were compromised tonight, how long would it take your team to know?

Contact Sensefinity to discuss an independent real-time monitoring and alerting layer for your cold-chain operations.
Sources

How Sensefinity Helps to decarbonise Airport Operations

Airport decarbonisation is often discussed in terms of new vehicles, chargers and renewable electricity. Those investments matter, but an airport first needs to understand how its existing equipment moves, waits, idles and consumes energy.

Ground operations involve baggage tractors, belt loaders, ground power units, pushback tractors, buses, catering vehicles, carts and many other mobile assets. Some are owned by the airport. Others belong to airlines or ground handlers. When their location and use are not visible across the operation, vehicles travel to find equipment, assets sit idle in the wrong place and fleets become larger than they need to be.

Sensefinity can provide the operational data behind a practical decarbonisation programme. Connected trackers and sensors show where equipment is, how it is being used and where energy is being wasted.

Stop driving around to find equipment

Searching for equipment creates emissions without creating value. A driver may cross the apron to collect a belt loader, discover that it has moved, then travel to another stand. Similar searches happen for baggage carts, GPUs, tools and non-motorised assets.

A Sensefinity tracker makes the asset visible on a shared operational map. Teams can identify the closest available unit and assign it before the next turnaround. Geofences can show whether equipment is at a stand, charging area, workshop or unauthorised location.

There is already evidence that this approach produces environmental benefits. Hong Kong International Airport described an IoT and LoRaWAN system used to locate more than 120 pieces of ground service equipment. The airport reported better operational efficiency and expected a 75% reduction in respirable suspended particulates associated with driving to find the equipment.

The principle is straightforward: if the airport removes unnecessary movement, it reduces fuel, local air pollution, noise and wear at the same time.

Identify idling, empty journeys and poor positioning

Location is only the start. Movement history can reveal repeated routes, excessive idle periods, empty journeys and equipment positioned far from where it will next be needed.

These patterns can be analysed by asset type, operator, stand, terminal or time of day. The airport can distinguish a vehicle that is essential to a busy turnaround from one that is moving because the operation lacks coordination.

Alerts can support immediate action. Analytics supports the larger decisions: changing staging areas, balancing equipment between handlers, redesigning routes or reducing the number of vehicles assigned to a shift.

IATA's Ground Ops of the Future programme identifies asset tracking, telematics and optimal resource allocation as tools for better efficiency and lower fuel consumption. Sensefinity provides the physical data needed to apply those ideas to each airport's actual operation.

Electrify the right equipment first

Replacing every diesel asset at once is rarely practical. Airports and ground handlers need to decide which equipment can move to electric power first and what charging infrastructure it will require.

A tracker can build a real duty-cycle record for each asset:

  • operating and idle hours;

  • distance and routes;

  • time between tasks;

  • overnight and daytime parking locations;

  • utilisation peaks;

  • time available for charging.

This data helps identify vehicles with predictable routes and sufficient charging windows. It also prevents over-specification. The airport can choose batteries and chargers based on observed use rather than assumptions.

After electrification, the same platform can monitor availability and charging behaviour. Operations teams can receive an alert when a vehicle is not charging as planned or when its expected energy level may be insufficient for the next assignment.

Build an operational carbon dashboard

Annual fuel totals are useful for reporting, but they do not explain where emissions originate or which operational change worked.

Sensefinity can combine asset telemetry with vehicle type, fuel, electricity and turnaround data. The resulting dashboard can estimate energy use and emissions by asset, operator, terminal, stand or flight activity.

This allows an airport to answer practical questions:

  • Which equipment creates the most avoidable movement?

  • Did a new staging policy reduce kilometres travelled?

  • Are electric assets replacing diesel activity or simply adding fleet capacity?

  • Which handler has the best utilisation rate?

  • How much idle time was removed this month?

These measurements can support Scope 1 reporting for airport-owned equipment and provide evidence for relevant Scope 3 collaboration with airlines and ground handlers. The platform does not replace a formal greenhouse-gas inventory. It improves the operational evidence behind it.

Extend asset life through condition monitoring

Decarbonisation also means obtaining more useful life from equipment and avoiding unnecessary replacement.

Sensors can record vibration, shock, temperature, movement and utilisation cycles. Maintenance teams can use abnormal patterns and actual operating hours to plan inspections based on condition rather than a fixed calendar alone.

This can reduce breakdowns, emergency maintenance journeys and spare-parts consumption. It also helps the airport use a smaller fleet more reliably because the condition and availability of each asset are known.

Start with a measurable 90-day pilot

An airport does not need to instrument the whole airfield before seeing value. A first deployment could place 50 to 100 trackers on baggage tractors, carts, belt loaders, GPUs and frequently misplaced equipment.

The baseline and pilot should measure:

  • kilometres travelled per turnaround;

  • idle hours;

  • time spent searching for equipment;

  • utilisation and availability;

  • fuel or electricity per operating hour;

  • delays caused by missing assets;

  • maintenance events;

  • estimated CO2 and local pollutants avoided.

The pilot creates a quantified case for wider tracking, fleet pooling, route changes and electrification. It also gives the airport, airlines and ground handlers a common operational picture.

Decarbonising airport operations is partly an energy transition, but it is also an information problem. Sensefinity makes the physical operation measurable, so airports can remove waste before buying more equipment and verify the effect of every change they make.

Learn more about Sensefinity's asset tracking platform, NB-IoT trackers and IoT technology.

Sources and further reading: IATA Ground Ops of the Future and Hong Kong International Airport's GSE tracking case.

How Sensefinity improves the Customer Journey in an Airport

Most airport technology is invisible to passengers until something goes wrong. A bag does not arrive. A wheelchair is somewhere in the terminal, but nobody can find it. A moving walkway stops during the morning rush. The passenger experiences each incident as a broken journey, even when the flight itself is on time.

Airports already collect large amounts of operational data. The gap is often between the digital plan and the physical asset: the baggage cart, wheelchair, container, vehicle or piece of equipment that has to be in the right place at the right time.

Sensefinity closes that gap with connected trackers, sensors and a cloud platform that makes airport assets visible. Location and condition data can be turned into alerts, estimated delivery times and operational decisions before a delay reaches the passenger.

Make baggage delivery more predictable

Baggage is one of the clearest points where airport operations become part of the customer journey. Passengers have little information between leaving the aircraft and seeing their suitcase on the reclaim belt.

A Sensefinity deployment can track baggage containers, ULDs, carts and exception baggage as they move from the aircraft to the terminal. The airport or ground handler can see whether a container has left the stand, reached the sorting area or remained stationary for too long. Geofences can flag movement into the wrong operational zone.

This does not require a tracker on every suitcase. Airports can begin with the shared assets that carry baggage and with flows where the cost of failure is highest: transfer bags, premium baggage, mobility equipment, oversized items or bags already identified as exceptions.

The same events can support passenger communication. Instead of a generic "baggage delayed" message, the airport can provide a useful status: the baggage has been unloaded, it is moving to the terminal, or delivery to the belt has started. Better information does not remove every delay, but it removes much of the uncertainty around it.

Find passenger assistance equipment when it is needed

A wheelchair may be available somewhere in the airport and still be unavailable to the passenger waiting at the gate.

Small, battery-powered trackers can make wheelchairs, electric assistance vehicles, baby strollers and other PRM equipment visible across the terminal. Dispatch teams can locate the nearest available unit instead of calling several colleagues or searching storage areas.

Historical data also shows where demand occurs. The airport can compare equipment availability with flight schedules, passenger assistance bookings and terminal peaks. Over time, this supports better positioning before the passenger arrives, rather than a search after the service is already late.

The result is a measurable improvement: shorter assistance waiting times, fewer missed handovers and higher use of the equipment the airport already owns.

Prevent facility failures from becoming passenger problems

Elevators, escalators, moving walkways, automatic doors and passenger boarding bridges are physical systems with operating patterns. Changes in vibration, temperature, movement or cycle time can provide an early warning that maintenance is required.

Sensefinity sensors can feed this condition data into the airport's maintenance process. Teams can investigate abnormal behaviour during a planned service window instead of responding only after equipment has stopped.

This is particularly important for passengers with reduced mobility. An elevator outage that is inconvenient for one passenger can make a route unusable for another. Condition-based maintenance supports a more reliable and accessible terminal without replacing the airport's existing maintenance platform.

Protect temperature-sensitive services

Passenger experience also depends on services that operate behind counters and closed doors. Airport pharmacies, medical rooms, catering areas, premium lounges, pet-handling facilities and some categories of baggage all have temperature or humidity requirements.

Sensefinity sensors can monitor these conditions continuously and send an alert when a threshold is crossed. Staff can intervene while there is still time to protect the product, medicine or animal, rather than discovering the problem during an inspection or complaint.

The platform can retain the event history as evidence of how an item or area was handled. Where several companies share responsibility, this provides a common operational record rather than separate spreadsheets and conflicting accounts.

Connect the airport without replacing every system

An airport is already an ecosystem of airline, handler, security, facilities and passenger systems. A useful IoT project should add physical visibility without demanding that the airport replace all of them.

Sensefinity's trackers communicate through technologies such as NB-IoT, LTE-M and GPS, while the platform can send alarms, reports and data to other applications. The airport can start with one defined problem and integrate the events that matter.

A practical first project could cover baggage carts, wheelchairs and selected high-value mobile assets in one terminal. During a 90-day pilot, the airport can measure:

  • time spent searching for equipment;

  • passenger assistance waiting time;

  • first-bag and last-bag delivery times;

  • assets unavailable at the point of demand;

  • incidents detected before a passenger complaint;

  • utilisation by location and time of day.

The customer journey improves when the physical operation becomes predictable. Bags, wheelchairs and equipment still have to move through a busy airport. Sensefinity gives the people running that operation the information to act sooner and gives passengers clearer answers while they wait.

Learn more about Sensefinity's Internet of Cargo, NB-IoT trackers and IoT technology.

The F-35 Shipment That Went to Hong Kong: Why Critical Components Need Verifiable Custody

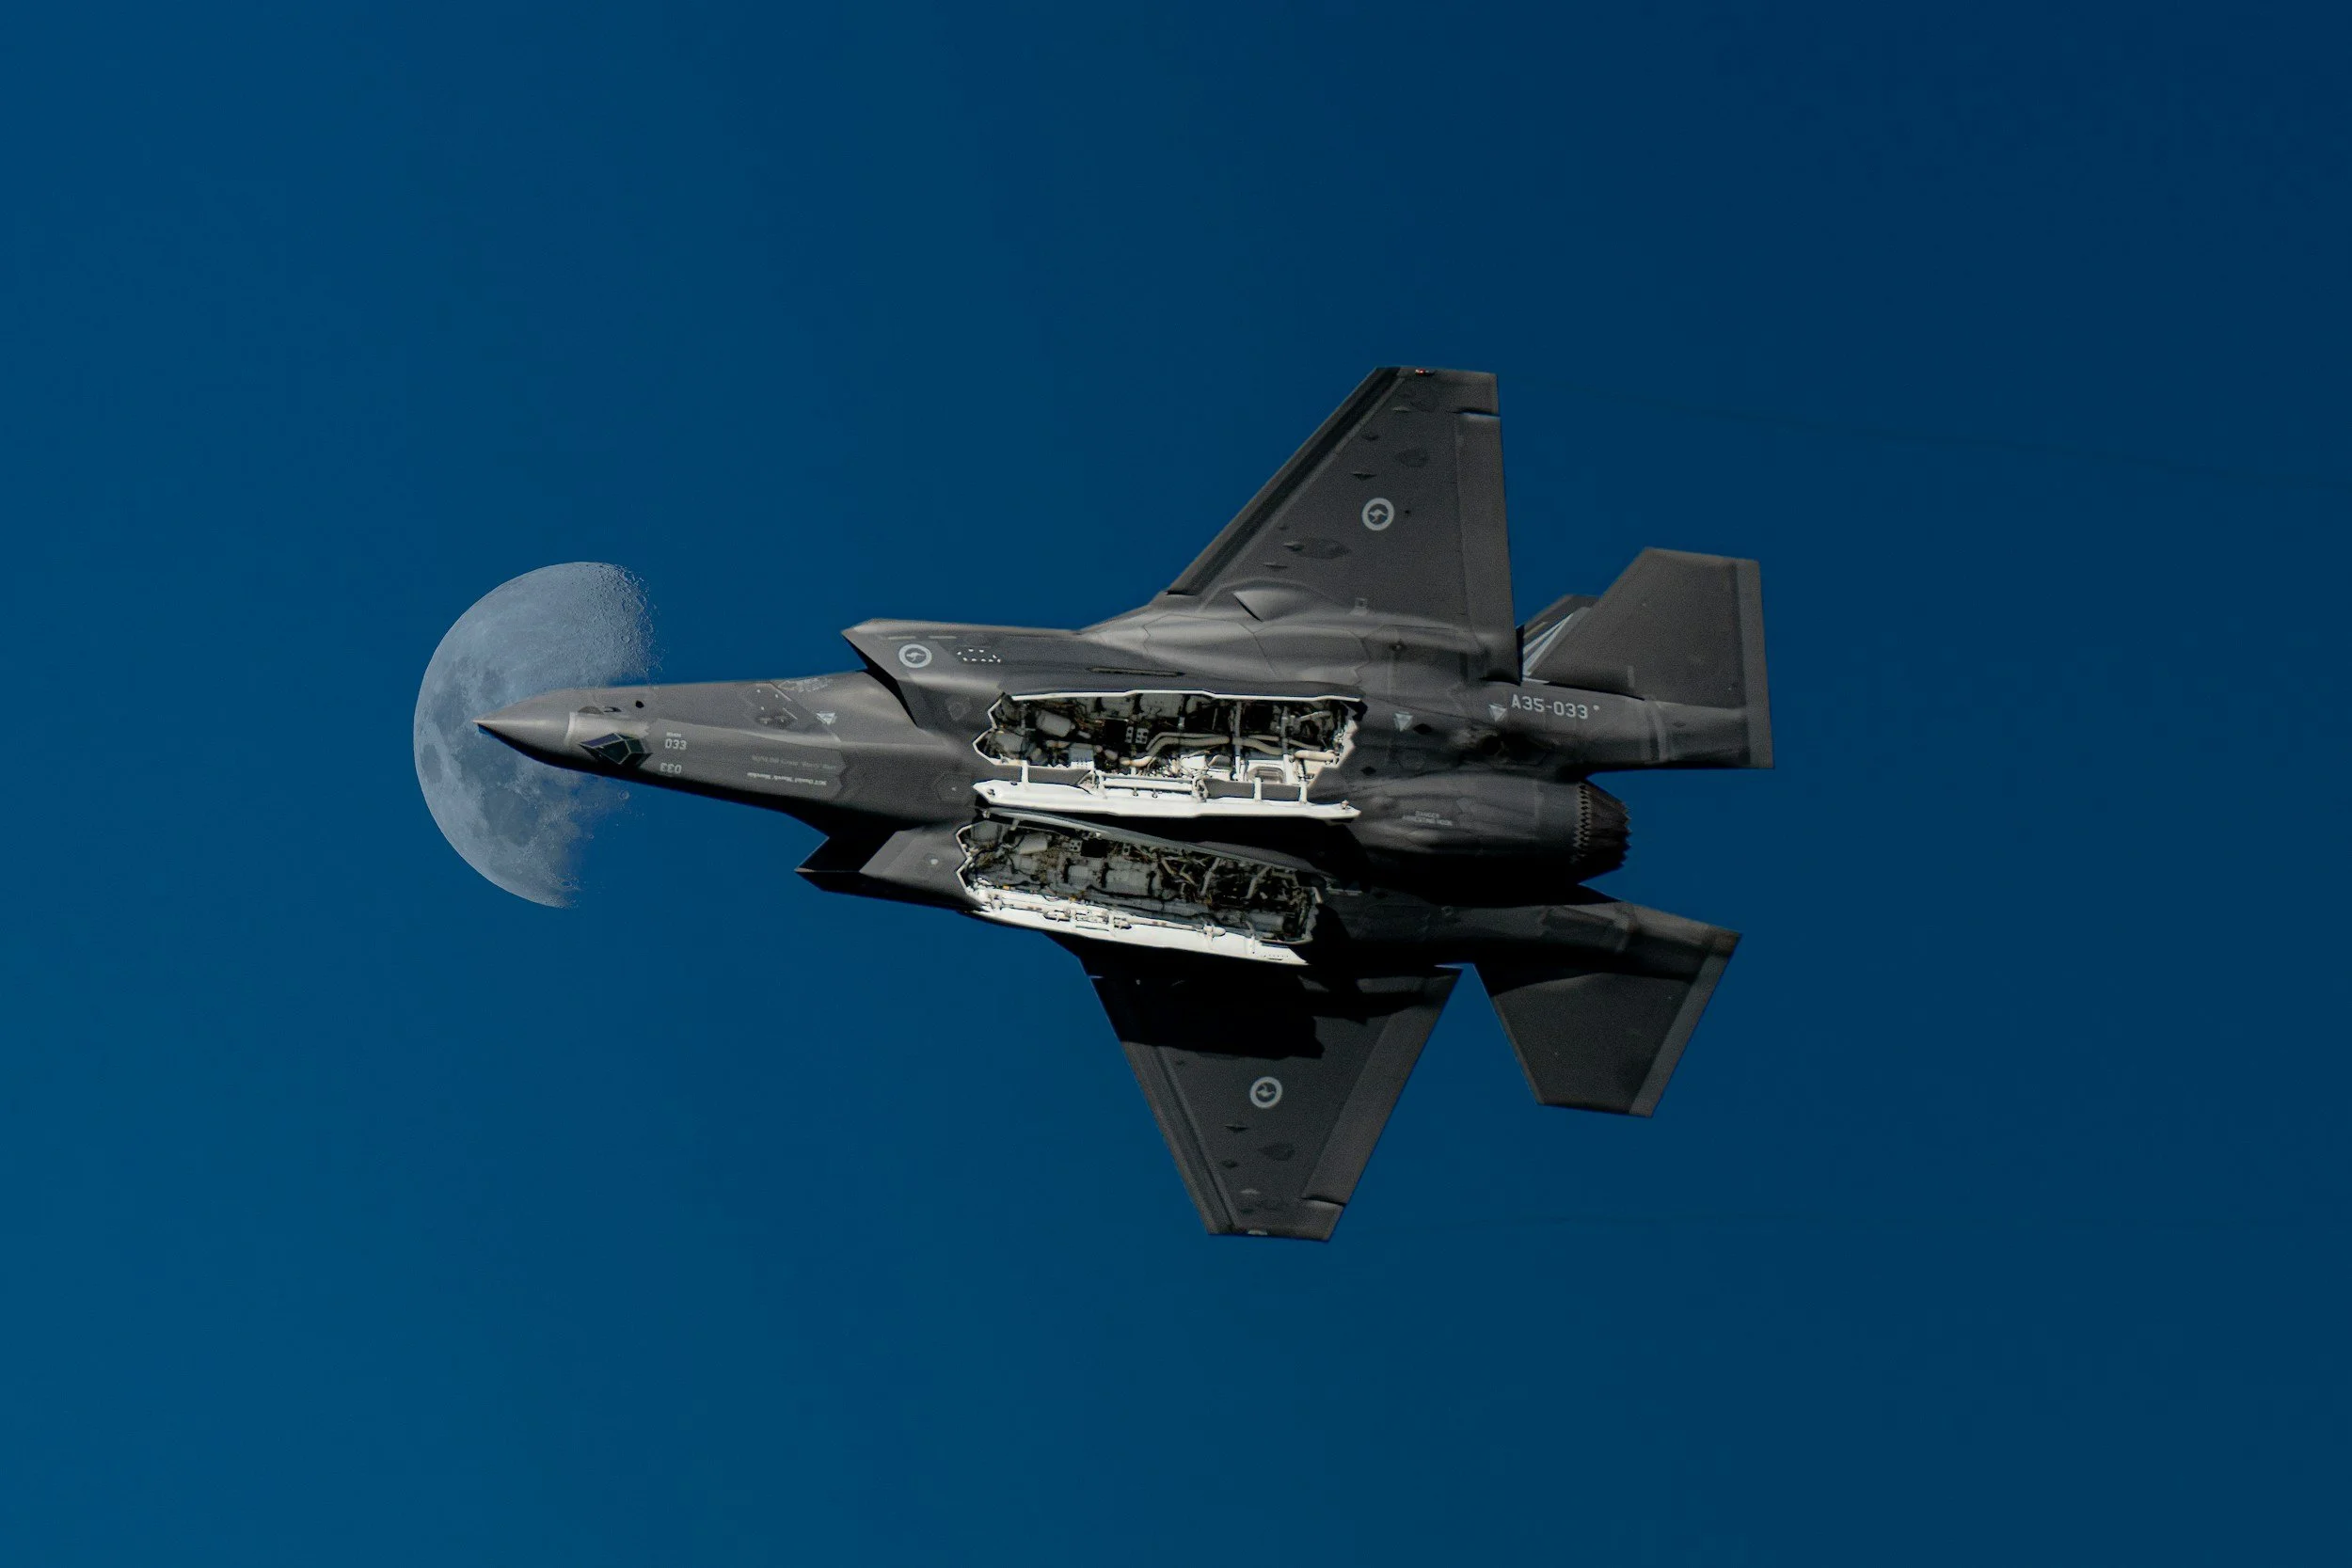
Australia confirmed on 22 September that unserviceable F-35 components shipped from the country for repair in the United States had instead been diverted to Hong Kong. The Australian government is assisting US authorities and Lockheed Martin with the investigation.

ABC reported that the shipment included a canopy incorporating radar-resistant technology and that an intermediary was responsible for transport. Australia’s defence minister, Richard Marles, also said that, according to his understanding, no technologically sensitive equipment had been lost. The reason for the diversion, the present location of every component and any access by a third party have not been publicly confirmed.

That distinction matters. This is not evidence that China obtained F-35 secrets. It is evidence of a custody-control failure serious enough to trigger government and congressional scrutiny.

A manifest records intent, not physical reality

A shipping document can say “United States” while the physical asset travels somewhere else. In a multi-party transport chain, information moves through maintenance teams, freight forwarders, airlines, customs agents and repair facilities. A wrong routing instruction, an unauthorised change or a simple mismatch between systems can survive several handoffs before anyone sees the full picture.

Critical logistics therefore needs independent evidence tied to the component itself—not only to an aircraft, booking or airway bill.

At Sensefinity, we connect the physical unit to its digital identity. An item-level or case-level sensor can report location, movement, opening, light exposure, separation from its assigned container and abnormal loss of communication. Geofences can cover approved routes, airports and jurisdictions. When the component leaves that policy envelope, the platform can create an exception while intervention is still possible.

An alert does not prove hostile intent. It reduces the time between divergence and response.

Learn more about Sensefinity Cargo Safety.

A destination change must become a signed custody event

Rerouting is normal in global logistics. Silent rerouting is not acceptable for controlled components.

Every destination or carrier change should require:

  • strong identity for the requesting party;

  • dual authorisation for high-risk exceptions;

  • an explicit reason and timestamp;

  • confirmation through a channel independent of the change request;

  • acceptance by the new carrier and consignee;

  • reconciliation with the component’s live telemetry.

Each physical handoff should bind the person, organisation, component identifier, seal, time and location. If the transport record says the United States while the sensor indicates Hong Kong, the mismatch should block automatic acceptance and open an investigation.

Blockchain makes later rewriting visible

Sensors show what happened in the physical journey. Blockchain can help preserve who authorised it, what each participant accepted and which record existed at a specific time.

The right design for sensitive supply chains is permissioned. Military or commercially restricted information does not need to be published on a public chain. Hashes, identities, document versions and timestamps can be anchored while operational detail remains off-chain under access control.

This creates a shared, tamper-evident chronology across organisations that may not share one database. An investigator can compare the original manifest, authorised route, sensor events, custody receipts and later changes without trusting a single party’s retrospective export.

Blockchain does not make bad input true, and it does not physically prevent diversion. It is effective when combined with authenticated sensors, strong approvals and an operational response process.

See how our Blockchain solution connects telemetry, identity and chain of custody.

Five controls critical shipments should adopt now

  1. Bind identity to the physical unit. Link every component, case and container to its sensor, seal, manifest and authorised destination.

  2. Monitor policy, not just position. Alert on prohibited jurisdictions, route deviations, unplanned transfers, opening and abnormal silence.

  3. Make changes explicit. Require dual approval and out-of-band confirmation for destination, carrier or consignee changes.

  4. Prove every handoff. Record strong identity, time, location, condition and counterparty acceptance at each custody transfer.

  5. Preserve the evidence. Keep raw telemetry and anchor approvals and versions in a permissioned, tamper-evident record with defined escalation and recovery procedures.

The lesson is broader than defence. Semiconductor equipment, prototypes, medical products, luxury goods and other high-value assets face the same gap between the route written in a system and the journey taken by the physical object.

Critical cargo should never be “somewhere in the network.” It should have a continuously verifiable identity, route and custodian.

Read the complete Prova analysis, including the confirmed facts and the limits of what is publicly known.

Sources

NB-IoT, LTE-M or Cat 1 bis? Choosing the right cellular link for real-world IoT

Choosing cellular connectivity for an IoT product is not a contest to find the newest acronym. It is a design decision about where the device will travel, how often it reports, how much data it sends, how long it must run and which networks are actually available along the route.

NB-IoT, LTE-M and LTE Cat 1 bis all use licensed cellular spectrum, but they solve different problems. NB-IoT and LTE-M are 3GPP low-power wide-area technologies introduced in Release 13. Cat 1 bis is a simplified version of LTE Cat 1 that uses one receive antenna instead of two.[1][3]

None is the universal winner. The right answer comes from the workload.

Three technologies, not three generations

It is tempting to arrange the options as a ladder: NB-IoT at the bottom, LTE-M in the middle and Cat 1 bis at the top. That misses the point.

NB-IoT is deliberately narrow. It gives small, infrequent messages a path through licensed networks while keeping device complexity and power demand low. LTE-M adds better mobility, responsiveness and throughput while retaining LPWA power-saving features. Cat 1 bis uses the broader LTE footprint and offers much more data capacity, but it is not classified as an LPWA technology by the GSMA.[1]

The comparison is closer to choosing a vehicle. A bicycle, a van and a truck can all move goods, but the payload and route decide which one makes sense.

Where NB-IoT has the advantage

NB-IoT is built for devices that sleep most of the time, wake up, send a small reading and return to sleep. 3GPP designed it for improved indoor coverage, large populations of low-throughput devices, low delay sensitivity, low device cost and low power consumption. It can run inside an LTE carrier, in the guard band or in dedicated spectrum.[2]

That profile fits applications such as:

  • meters and tank-level sensors;

  • environmental monitoring;

  • stationary cold-chain sensors;

  • returnable packaging that reports occasionally;

  • assets stored in basements, warehouses or other difficult radio locations.

Its narrow 180 kHz carrier and coverage-enhancement modes help when penetration matters more than speed. Power Saving Mode and extended discontinuous reception can keep the modem asleep for long periods, although real battery life still depends on signal quality, reporting frequency, retries, temperature, battery chemistry and operator settings.[1]

The trade-off is responsiveness. NB-IoT is intended for small payloads and delay-tolerant traffic. Classic Release 13 deployments do not provide the seamless handover expected by fast-moving trackers; later releases added mobility improvements, but support depends on the module and network. It is not the first choice for frequent position updates, large firmware downloads or an asset that continuously crosses cell boundaries.

Where LTE-M has the advantage

LTE-M, also called Cat-M1 in its first widely deployed form, keeps many LPWA benefits while behaving more like mobile LTE. It supports handover between cells, lower latency and higher throughput than NB-IoT. This is useful when the device is attached to a pallet, trailer, container, vehicle or piece of equipment that keeps moving.

LTE-M is a good fit for:

  • mobile asset and cargo tracking;

  • regular GNSS position and sensor updates;

  • alarms that need a faster response;

  • larger over-the-air firmware updates;

  • wearables and safety devices;

  • products that may need voice, where the operator has enabled VoLTE for LTE-M.

The GSMA describes LTE-M as an LPWA technology with low device complexity, low power use, extended coverage, low latency and support for high connection density.[1] It also supports PSM and eDRX, so a well-designed tracker can spend most of its life asleep and wake only when movement, a schedule or a sensor event requires a report.

LTE-M's weakness is not the radio specification. It is availability. Operators have deployed NB-IoT and LTE-M unevenly, and roaming support is not identical to ordinary smartphone LTE roaming. The GSMA's launch inventory shows substantial commercial deployment of both technologies, but a country appearing on a list does not prove that the required band, operator, roaming agreement or power-saving feature will work for a specific device.[5]

Where Cat 1 bis has the advantage

LTE Cat 1 bis takes a different route. It keeps Cat 1's data capability and standard LTE operation but removes the second receive chain and antenna. That reduces hardware complexity, board area and cost. The price is a coverage penalty compared with two-antenna Cat 1, particularly near the cell edge.[1][3]

Cat 1 bis can reach the Cat 1 class maximum of about 10 Mbps downlink and 5 Mbps uplink; commercial modules advertise those figures for supported networks.[4] That capacity changes what an IoT device can do:

  • transfer larger firmware images more quickly;

  • upload richer diagnostics or frequent telemetry;

  • support payment terminals and industrial gateways;

  • send audio or limited image data where the application requires it;

  • provide tracking and telematics across ordinary 4G LTE coverage.

It also supports mobility and standard LTE handover. Because it does not need the network to activate a separate NB-IoT or LTE-M radio feature, Cat 1 bis can be easier to deploy across regions where 4G LTE is present but LPWA coverage is incomplete.[1][3]

The compromise is power. New Cat 1 bis modules may support PSM and eDRX, but Cat 1 bis is not an LPWA category and network support for those modes is not uniform. Its faster transfer can reduce radio-on time for a large payload, yet a small sensor sending a few bytes may still get better energy economics from NB-IoT or LTE-M. The only reliable answer comes from measuring the complete duty cycle on the target networks.

The comparison in one view

NB-IoT

  • Primary strength: deep coverage and very low power for small, infrequent messages.

  • Mobility: best for stationary or slowly changing deployments; support for later-release mobility features varies.

  • Typical data: tiny, delay-tolerant telemetry.

  • Power profile: usually strongest for long sleep cycles and sparse reporting.

  • Voice: not supported.

  • Coverage dependency: requires an operator's NB-IoT deployment and compatible bands.

  • Best starting point: static sensors, metering, storage and hard-to-reach locations.

LTE-M

  • Primary strength: low-power mobility with moderate throughput and faster response.

  • Mobility: seamless handover between cells.

  • Typical data: regular telemetry, GNSS positions, alarms and manageable firmware updates.

  • Power profile: a strong balance of battery life and mobile operation.

  • Voice: possible when the operator supports VoLTE on LTE-M.

  • Coverage dependency: requires LTE-M deployment, compatible bands and suitable roaming agreements.

  • Best starting point: cargo and asset tracking that moves between cells.

LTE Cat 1 bis

  • Primary strength: higher throughput across ordinary LTE infrastructure.

  • Mobility: standard LTE mobility and handover.

  • Typical data: frequent telemetry, large firmware images, logs, audio or limited image data.

  • Power profile: sleep modes are possible, but active and network behaviour need closer power budgeting.

  • Voice: possible on some modules and operator profiles.

  • Coverage dependency: uses standard LTE, but bands, certification and roaming still need validation.

  • Best starting point: higher-data IoT or global products where LTE-M availability is insufficient.

These are design tendencies, not procurement guarantees. A module data sheet cannot tell you whether a roaming SIM will access a feature in a particular port, warehouse or border corridor.

What to test before choosing

A connectivity decision should begin with a route and workload model.

Map the real network footprint. Check every country, operator and LTE band in the planned deployment. Test roaming, not just home-network attachment. An operator may support a technology domestically but restrict access to roaming devices.

Model the complete energy budget. Include network search, registration, TLS setup, retransmissions, GNSS acquisition, sensor warm-up and firmware downloads. The lowest sleep current does not rescue a device that repeatedly searches for a missing network.

Use the real payload. Protocol headers and security handshakes may be larger than the sensor message. Compression, batching and event-driven reporting can change the best radio choice.

Plan firmware updates on day one. A product expected to remain deployed for years will need security and application updates. Estimate the worst-case image size, transfer time and energy cost before fixing the modem architecture.

Test cell edges and movement. Laboratory signal levels do not reproduce a metal container, a refrigerated trailer, a basement or a device moving between countries. Antenna placement and enclosure design can matter as much as the modem category.

What this means for cargo and asset tracking

A stationary temperature logger in a warehouse and a high-value shipment crossing five countries are both IoT devices, but they do not have the same connectivity problem.

NB-IoT can be the right choice when the asset remains within known coverage, messages are small and long battery life has priority. LTE-M is often the stronger fit when a tracker moves, reports position and condition regularly, and must keep sessions alive through cell changes. Cat 1 bis becomes attractive when the route has broad LTE but inconsistent LTE-M availability, or when the device needs larger updates and richer data.

Some products should support more than one radio mode. A multimode design can prefer LTE-M for mobility, use NB-IoT where available for sparse telemetry, or select Cat 1 bis for a separate high-throughput product family. That flexibility has a cost in hardware, certification, firmware and testing, so it should solve a real deployment problem rather than become a feature-list exercise.

At Sensefinity, connectivity is part of the Internet of Cargo, not the whole solution. The useful outcome is verified information about location, temperature, humidity, shock, opening events and custody, delivered with the right balance of coverage, energy and cost. Our NB-IoT trackers and cargo-monitoring work begin with that operational question: what must the customer know, where and how quickly?

The decision rule

Choose NB-IoT when the message is small, the device sleeps for long periods and coverage penetration matters more than mobility or speed.

Choose LTE-M when the asset moves and the application needs LPWA power consumption with handover, lower latency and enough throughput for regular tracking and updates.

Choose Cat 1 bis when higher data rates and the ordinary LTE footprint matter more than achieving the lowest possible power profile.

Then verify the choice on the target operators, bands, routes and enclosures. A technology comparison narrows the field. Field testing makes the decision.

Sources

[1] https://www.gsma.com/solutions-and-impact/technologies/internet-of-things/wp-content/uploads/2024/10/Mobile-IoT-in-a-5G-Future-Final.pdf — Mobile IoT in a 5G Future — GSMA [2] https://3gpp.org/news-events/3gpp-news/niot — NarrowBand IoT — 3GPP [3] https://www.u-blox.com/en/blogs/insights/lte-cat-1bis — LTE Cat 1bis — u-blox [4] https://www.quectel.com/product/lte-cat-1-bis-eg916q-gl — LTE Cat 1 bis EG916Q-GL — Quectel [5] https://www.gsma.com/solutions-and-impact/technologies/internet-of-things/mobile-iot-commercial-launches — Mobile IoT network launches — GSMA

When Cold-Chain Service Cannot Be Proven: The Graciosa Fish Case

Complaints reported on 9 September 2026 about cold handling for fish air cargo travelling to and from Graciosa Island raise a simple but important question: how can an operator prove that the paid refrigeration service was actually delivered at every stage? The allegations still require investigation, but the underlying visibility gap is already clear.

An invoice is not a temperature record

A service charge confirms that refrigeration was purchased. It does not show when a fish lot entered cold storage, its temperature while waiting or transferring, how long it remained outside its permitted range, or who held custody when a deviation occurred.

For perishable cargo, those facts must travel with the lot. Sensefinity's cold-chain monitoring connects temperature, location and time data so teams can receive alerts while intervention is still possible—not discover a broken chain only after delivery.

Each transfer needs evidence

The risk is not limited to the flight. It can appear at the dock, during transport to the airport, while awaiting screening, at an intermediate stop or at final delivery. Every handover needs an accountable party, defined thermal limits and a continuous record.

Sensor data can be linked to a tamper-resistant blockchain audit trail, creating evidence of what happened, where and when. Blockchain does not refrigerate fish; it helps prove whether the cold-chain process was followed.

Read the full Prova analysis

Our partner publication Prova examines the Graciosa case in greater detail, including how real-time alerts, lot-level traceability and a Digital Product Passport can support release, inspection, quarantine and claims decisions.

Read “Fish cold chain in the Azores: proving the service was delivered” on Prova.

The lesson is practical: for temperature-sensitive cargo, availability is not enough. The supply chain must be able to demonstrate, operation by operation, that the service was delivered and the product remained within its agreed conditions.

A New Destination Is a New Custody Act

A freight destination is not just an address field. Changing it alters the authorised route, the intended consignee and the point at which custody passes to another party. When that decision lives only in an email, a phone call or an overwritten TMS field, a fraudulent redirection can look like routine administration.

Replace silent edits with signed events

We believe every destination change should create a new custody act tied to the lot: previous destination, new destination, reason, requesting organisation and person, timestamp, approval policy and a cryptographic reference to the preceding event. The old instruction remains visible. Revocations, refusals and corrections become additional events rather than rewritten history.

Strong authentication must come before signature. For sensitive loads, that means step-up or multi-factor authentication, explicit confirmation of what is being signed and dual approval when value, product or route justifies it. A valid login is not enough; the signer must also be authorised to redirect that specific lot.

Anchor proof, protect commercial data

With Sensefinity's blockchain layer, the signed document can remain access-controlled off-chain while its hash, version and timestamp are anchored in a tamper-resistant history. Authorised partners can verify that the instruction presented is the one that was signed and identify what came before it without publishing sensitive commercial details.

Blockchain cannot prove that a bad instruction was true or prevent a compromised credential. Its value is narrower and more useful: changes, sequence and conflicts become much harder to hide.

Connect authorised intent to physical movement

The signed act defines what should happen. Cargo telemetry shows what is happening. Sensefinity's Cargo Safety capabilities can detect unplanned stops and unauthorised access and support asset-level tracking. Comparing those signals with the latest authorised destination creates an actionable exception when a load leaves its approved route before a valid change exists.

Read the full Prova article

The full Prova analysis explains the event model, authentication and authorisation controls, blockchain anchoring, a seven-step operating workflow and how this approach aligns with the move toward authenticated, auditable freight data.

Read “A destination change is a custody act — and it should be signed” on Prova.

A destination change should never erase the past. It should add a signed, attributable and verifiable decision to the lot's custody history.

The $647,420 Nike Pickup That Looked Legitimate — Until It Wasn’t

A driver arrived at a Memphis facility with documents that appeared sufficient to collect a Dallas-bound shipment of Nike merchandise. The cargo left the dock. But the driver was not completing the authorized movement, the paperwork was fraudulent, and the shipment headed towards the Chicago area instead.

The fictitious pickup happened on 21 August 2026. Nike contacted the Cook County Sheriff’s Police Organized Retail Crime Unit two days later, and investigators ultimately recovered approximately $647,420 in merchandise at a distribution facility in Des Plaines, Illinois, together with a stolen trailer. At the time of the report, no arrests or charges had been announced and the investigation remained active.[1]

This was not a failure of a lock. It was a failure of trust: the wrong person presented documents that looked right long enough for legitimate staff to release valuable cargo.

When a document looks right but custody is wrong

Traditional shipping documents describe an intended transaction. They do not necessarily prove that the person standing at the dock is the person currently authorized to execute it.

A convincing PDF, bill of lading or pickup reference can be copied, altered or generated from compromised information. The Nike incident is especially instructive because the shipment did not first disappear from an unattended parking area. It was handed over at origin after false paperwork made an unauthorized collection appear legitimate.[1]

It also sits within a wider pattern. In a separate Nike case, federal prosecutors alleged that unauthorized UPS labels were used to divert products from the company’s Memphis distribution operation. Reporting on that case describes “ghost labels” covering original shipping labels and redirecting packages to private addresses; those allegations have not been proven in court.[2]

The common weakness is clear: when operational truth lives only in editable labels, emails and documents, whoever can reproduce the appearance of authority may be able to redirect the physical goods.

Blockchain should verify the handover, not archive the fraud

Simply uploading a document to a blockchain is not enough. If false information is accepted at the start, an immutable database only preserves a false statement.

The useful model is different: create a verifiable digital chain of custody and require every physical handover to match its current authorized state. Before a warehouse releases a shipment, the system should be able to answer five questions:

  1. Which exact shipment is being collected? A unique digital identity binds the order, cargo unit, pallet or container to the operational record.

  2. Who is authorized right now? The approved carrier, driver, vehicle and pickup window are recorded by trusted parties, rather than inferred from a document presented at the gate.

  3. Has anything changed? A destination, carrier or collection instruction cannot be silently overwritten. A new authorization becomes a visible, time-stamped event.

  4. Is this handover happening in the expected place and time? A one-time release credential can be bound to the shipment, facility and pickup window.

  5. What happened after release? Independent IoT data confirms departure, movement and route exceptions instead of relying only on status messages from the party holding the load.

In that model, a counterfeit document is no longer the authority. It is merely a claim that must match the shared, verifiable record.

What the Nike pickup could have looked like

Imagine the same collection with digitally verified custody controls.

At the Memphis gate, the operator scans the shipment identifier and the driver’s one-time pickup credential. The system checks both against the latest authorization recorded for that shipment. If the driver, carrier, vehicle, destination or collection window does not match, the cargo is not released and the discrepancy is escalated through a known channel.

If all checks pass, the handover is signed as a new custody event. A cargo-level tracker then confirms when the load leaves the facility. A Dallas-bound shipment moving towards Chicago crosses a route or geofence rule, generating an alert while intervention may still be possible.

The incident report says investigators recovered the Nike merchandise after the diversion was identified.[1] A verified release process could have moved the decisive control point earlier—from recovery after the theft to refusal at the dock. No technology can guarantee prevention, but forged paperwork becomes much less useful when it cannot satisfy the digital authorization and physical-event checks required for release.

Sensefinity connects the record to the real cargo

The hard part of supply-chain blockchain is connecting digital claims to physical events. Sensefinity addresses that gap with IoT “oracles”: trackers and sensors that collect cargo location and environmental data, register it in the Sensefinity platform and can also write selected information to a logistics blockchain. Authorized partners can access the shared record without requiring direct access to one another’s internal IT systems.[3]

Our Blockchain solution provides the tamper-evident event layer. Our NB-IoT trackers locate assets on land and at sea and can issue alerts when an asset enters or leaves a configured geofence.[4]

Together, those capabilities support a stronger release and custody process:

  • digitally signed shipment and pickup authorizations;

  • an auditable history of instruction changes;

  • verified handovers between shipper, carrier, warehouse and receiver;

  • cargo-level location evidence independent of the truck or transport paperwork;

  • immediate alerts for unauthorized departure, route deviation or unexpected arrival;

  • a provenance record that follows the goods beyond a single logistics provider.

Trust the verified event, not the convincing document

Fictitious pickup succeeds in the gap between what a document says and what the operation can prove. Closing that gap requires more than checking logos, signatures and reference numbers. It requires a shared source of truth, a controlled handover and independent evidence from the cargo itself.

The $647,420 Nike recovery had a positive outcome. The more important objective for the next shipment is to make forged paperwork fail before the doors close and the truck leaves.

Talk to Sensefinity about combining IoT visibility, geofencing and blockchain-backed chain of custody for high-value cargo.

Sources

  1. $647K Nike cargo recovered near Chicago after fraudulent Memphis pickup — FreightWaves

  2. How Nike insiders were charged in a lucrative sneaker theft conspiracy — Los Angeles Times

  3. Sensefinity Logistics Blockchain

  4. Sensefinity NB-IoT Trackers

EPCIS in 2026: The State of Supply Chain Event Data

Supply chains have no shortage of data. They have a shortage of data that different companies can interpret in the same way.

That is the problem EPCIS was built to solve. GS1 describes EPCIS as its flagship standard for sharing the what, when, where, why and how of products and assets across organisations. EPCIS 2.0 extends that event model to sensor readings, certifications, JSON/JSON-LD, REST interfaces and GS1 Digital Link identifiers.[1]

This report assesses where the standard stands in 2026, what is driving implementation, and where projects still break down. It is a desk-research snapshot, not a vendor adoption survey. Our evidence comes from current GS1 specifications and public regulatory material.

The 2026 snapshot

Signal What the evidence says Industry implication Standard maturity EPCIS 2.0 was ratified in June 2022; its implementation guideline followed in March 2023 and the GS1 EPCIS Sandbox launched in February 2024.[1] The technical foundation is established. The main risk has moved from specification maturity to implementation discipline. Condition data EPCIS 2.0 can carry timestamped sensor data, including readings used in cold chains and industrial IoT.[1] Location events and temperature evidence can travel in one interoperable event stream. Certification data The standard supports certification details associated with products, organisations, locations, harvests and shipments.[1] Compliance evidence can be linked to the event where it matters rather than stored in an isolated document repository. API accessibility JSON/JSON-LD and REST capture/query interfaces are part of EPCIS 2.0.[1] Integration no longer has to start with XML-heavy, batch-only architecture. Regulatory pull The FDA Food Traceability Rule requires covered actors to retain Key Data Elements linked to Critical Tracking Events and provide requested information to FDA within 24 hours.[2] Regulated traceability is becoming an event-data problem, even where the law does not mandate EPCIS by name. DPP convergence The EU Digital Product Passport is being introduced progressively and will carry lifecycle, origin, material and environmental information for selected product groups.[11] Product master data and supply chain events will increasingly need a common identity layer.

Our finding: EPCIS covers five evidence layers, but governance remains outside the standard

We reviewed EPCIS 2.0 against five practical evidence layers required by modern cargo and product programmes.

Evidence layer EPCIS 2.0 coverage What still has to be designed Identity Native support through GS1 identifiers and Digital Link URI syntax.[1] Identifier ownership, granularity and partner onboarding. Business events Native event model for status, movement, transformation, aggregation and chain of custody.[1] A shared event vocabulary and rules for late or corrected events. Physical condition Native sensor-data support.[1] Device calibration, sampling frequency, alert thresholds and proof that a sensor remained attached to the cargo. Claims and certifications Native certification fields.[1] Who may issue a claim, how it expires and how it is revoked. Exchange JSON/JSON-LD and REST interfaces.[1] Access control, commercial permissions, retention and cross-company service levels.

The conclusion is useful because it separates a standards question from an operating-model question. EPCIS can express all five layers. It cannot decide which partner is trusted, how often a sensor should report, who pays for data retention or which event wins when two systems disagree.

Regulation is pushing companies toward event-level traceability

The strongest implementation pressure is no longer a generic promise of visibility. It is the need to reconstruct specific product histories quickly.

The FDA's Food Traceability Rule applies additional recordkeeping to foods on the Food Traceability List. Covered organisations must associate Key Data Elements with Critical Tracking Events and be able to provide the information to FDA within 24 hours or another agreed period.[2] GS1's own food-safety guidance maps GTIN, GLN and EPCIS event data to this need for product, location and movement records.[18]

The compliance date was originally January 20, 2026. FDA subsequently proposed a 30-month extension to July 20, 2028, and Congress directed the agency not to enforce the rule before that date.[2] That extension is preparation time, not a reason to postpone architecture. Partner identifiers, event semantics and exception workflows usually take longer than the API connection.

Europe is creating a second source of pressure. Under the Ecodesign for Sustainable Products Regulation, Digital Product Passports will be introduced through product-specific rules. The Commission lists batteries first, followed by product groups such as textiles, iron and steel, construction products and others.[8][11] A passport tells stakeholders what a product is and what must be known about it. EPCIS can supply the time-ordered operational evidence of what happened to it.

The adoption gap is not capture. It is continuity.

Most pilots can generate a shipping event. Far fewer can maintain a trustworthy history through repacking, consolidation, subcontracted transport and handover to another platform.

Four gaps appear repeatedly:

  1. Identity breaks at aggregation. A pallet identifier is recorded, but the link between item, case, pallet and container is incomplete.

  2. Condition data lacks business context. A temperature reading exists, but the system cannot say which shipment leg, custody holder or product lot it belongs to.

  3. Partners use different event meanings. "Received" may mean arrival at the gate, unloading, quality acceptance or ERP posting.

  4. Corrections are not governed. Event histories need a controlled way to handle duplicates, delayed data and amended records without erasing the audit trail.

EPCIS has the structures needed to address these problems. Implementers still need to agree on the operating rules.

A practical 90-day EPCIS readiness test

A company does not need a multi-year transformation programme to learn whether its data is ready. A useful first test follows one real shipment and asks five questions:

  • Can every tracked object and logistics unit be identified consistently?

  • Can the business record packing, shipping, receiving and transformation events using shared vocabulary?

  • Can sensor readings be tied to the correct object, place and time?

  • Can one external partner query only the events it is authorised to see?

  • Can the team reconstruct the shipment history without manually joining spreadsheets?

If any answer is no, the pilot has identified a concrete interoperability gap. That is more valuable than a polished dashboard built on ambiguous data.

Where Sensefinity fits

Sensefinity already supports EPCIS supply chain events and can combine them with location, temperature and humidity data. Our NB-IoT trackers create observations from the physical journey; EPCIS gives those observations a shared business context.

The result is not simply another track-and-trace screen. It is an event history that can be exchanged with customers, suppliers and compliance systems without forcing every participant into the same application.

What to watch next

During the next implementation cycle, three developments deserve attention:

  • convergence between EPCIS event histories and Digital Product Passport records;

  • practical use of sensor and certification fields beyond proof-of-concept projects;

  • partner governance, especially access rights, event correction and long-term availability.

The standard is ready enough. The differentiator in 2026 is whether companies can keep identity, condition and custody evidence connected after cargo leaves their own system.

Methodology and limitations

This report was prepared on September 5, 2026 from public GS1, FDA and EU sources. The readiness matrix is Sensefinity's analysis of features documented in EPCIS 2.0; it is not an adoption-rate survey. We found no authoritative global count of production EPCIS 2.0 deployments and have not invented one.

Sources

[1] https://www.gs1.org/standards/epcis — EPCIS & CBV | GS1 [2] https://www.fda.gov/food/food-safety-modernization-act-fsma/fsma-final-rule-requirements-additional-traceability-records-certain-foods — FSMA Food Traceability Rule | FDA [8] https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX%3A32024R1781 — Regulation (EU) 2024/1781 (ESPR) [11] https://single-market-economy.ec.europa.eu/single-market/digital-product-passport_en — Digital Product Passport | European Commission [18] https://gs1.org/public-policy/leveraging-GS1-standards-to-meet-key-food-safety-challenges — Leveraging GS1 standards for food safety | GS1

Fewer Thefts, Twice the Losses: The $304.6 Million Visibility Gap

Cargo theft incidents fell in the second quarter of 2026. The financial damage did not.

Verisk CargoNet documented 677 supply-chain theft incidents across the United States and Canada in Q2 2026, down 26% from the same quarter a year earlier. Yet estimated losses rose from $135.7 million to $304.6 million. Among incidents with a reported commodity value, the average reached $564,009.

This is not a contradiction. It is a warning: organized groups do not need to steal more freight when they can identify and divert the right freight.

For shippers of enterprise technology, metals, pharmaceuticals, food and other high-value goods, the new risk is concentration. A single compromised shipment can now erase the benefit of dozens of successful deliveries.

The shipment has become the target

CargoNet’s analysis points to continued targeting of enterprise computer equipment, networking components, cryptocurrency-mining hardware and industrial metals. These goods often travel through conventional logistics networks even when the value inside a trailer reaches several million dollars.

That creates a dangerous mismatch: extraordinary cargo protected by ordinary visibility.

A transport-management system may confirm that a truck was assigned. A carrier portal may show that a delivery is in progress. Neither necessarily proves that the valuable pallet is still with the expected vehicle, following the authorized route or remaining under the correct custody.

The distinction matters because modern cargo theft is increasingly strategic. CargoNet reports that business-email compromise and shipment misdirection remain important access points. Criminals can use a compromised account to identify valuable loads, impersonate trusted parties and alter shipment instructions while appearing legitimate.

In that environment, tracking the journey only at dispatch and delivery leaves too much time—and too many handovers—unobserved.

From vehicle visibility to cargo visibility

The answer is not one more status call. It is an independent data layer attached to the asset that matters.

Sensefinity’s NB-IoT trackers and sensors are designed to locate assets on land and at sea, record environmental conditions and generate alerts when an asset enters or leaves a configured geofence. Depending on the use case, the monitored asset can be a container, a pallet, a crate or the cargo itself.

This changes the security model in four practical ways:

  • Independent location: the shipment can report its own position instead of relying only on the tractor, trailer or driver’s phone.

  • Geofence alerts: an unexpected departure from an authorized corridor, yard or destination can be flagged while intervention is still possible.

  • Condition monitoring: temperature and humidity thresholds help reveal whether sensitive cargo remained within specification during a diversion or delay.

  • Datalogging and auditability: a continuous history gives operations, insurers and investigators evidence of where the asset moved and under which conditions.

No single technology prevents every theft. Carrier verification, access controls, secure communications and trained people remain essential. Cargo-level IoT complements those controls by reducing the period in which a diverted shipment is invisible.

Why response time determines recovery

High-value cargo moves quickly after a successful theft. Loads may be transferred, split, relabelled or routed into established resale channels. The longer a shipper waits to discover a deviation, the less useful yesterday’s location becomes.

Real-time alerts turn detection into an operational event rather than a reconciliation problem. If an asset exits a planned geofence or fails to arrive where expected, the shipper can investigate immediately, preserve the movement history and share actionable information with security partners.

The goal is not simply to know that a loss occurred. It is to know soon enough to change the outcome.

Proof across every handover

Location answers “where?” High-risk supply chains must also answer “what happened?” and “who had custody?”

Sensefinity’s IoT data can also be registered in a logistics blockchain, creating a traceable record of location and environmental conditions such as temperature, humidity and shock. This combination links physical events to a shared digital history.

For insurers and cargo owners, that evidence can support faster incident reconstruction. For customers, it can strengthen confidence that a shipment followed the expected route and remained within agreed conditions. For regulated or sensitive goods, it helps replace assumptions with verifiable data.

The lesson behind $304.6 million

The Q2 figures show why incident counts alone can be misleading. Fewer thefts did not produce lower risk because criminals concentrated on more valuable cargo and more sophisticated methods.

Supply-chain security must respond in the same way: focus protection on the shipment, not only on the vehicle; detect deviations as they happen, not after delivery fails; and preserve evidence across every handover.

The next loss may not come from more crime. It may come from one carefully selected load moving through one avoidable blind spot.

Sensefinity turns containers, pallets and cargo into connected assets—helping companies see where their goods are, understand their condition and act when the journey no longer matches the plan.

Talk to Sensefinity about cargo-level visibility.

Sources

  • Verisk CargoNet, “Cargo Theft Losses More Than Double to $304 Million in Q2 Despite a Drop in Thefts,” 6 August 2026: https://www.globenewswire.com/news-release/2026/08/06/3340253/0/en/cargo-theft-losses-more-than-double-to-304-million-in-q2-despite-a-drop-in-thefts-driven-by-high-value-metals-and-technology-heists.html

  • Sensefinity, “NB-IoT Trackers”: https://www.sensefinity.com/nbiot-trackers

  • Sensefinity, “Blockchain”: https://www.sensefinity.com/blockchain